The Open AI Stack Is Splitting Into Models, Runtimes, and Permanence Layers
Qwen-Image-2.1, AX, and Pirate Face show an open AI stack separating creation, agent execution, and model distribution into distinct layers.
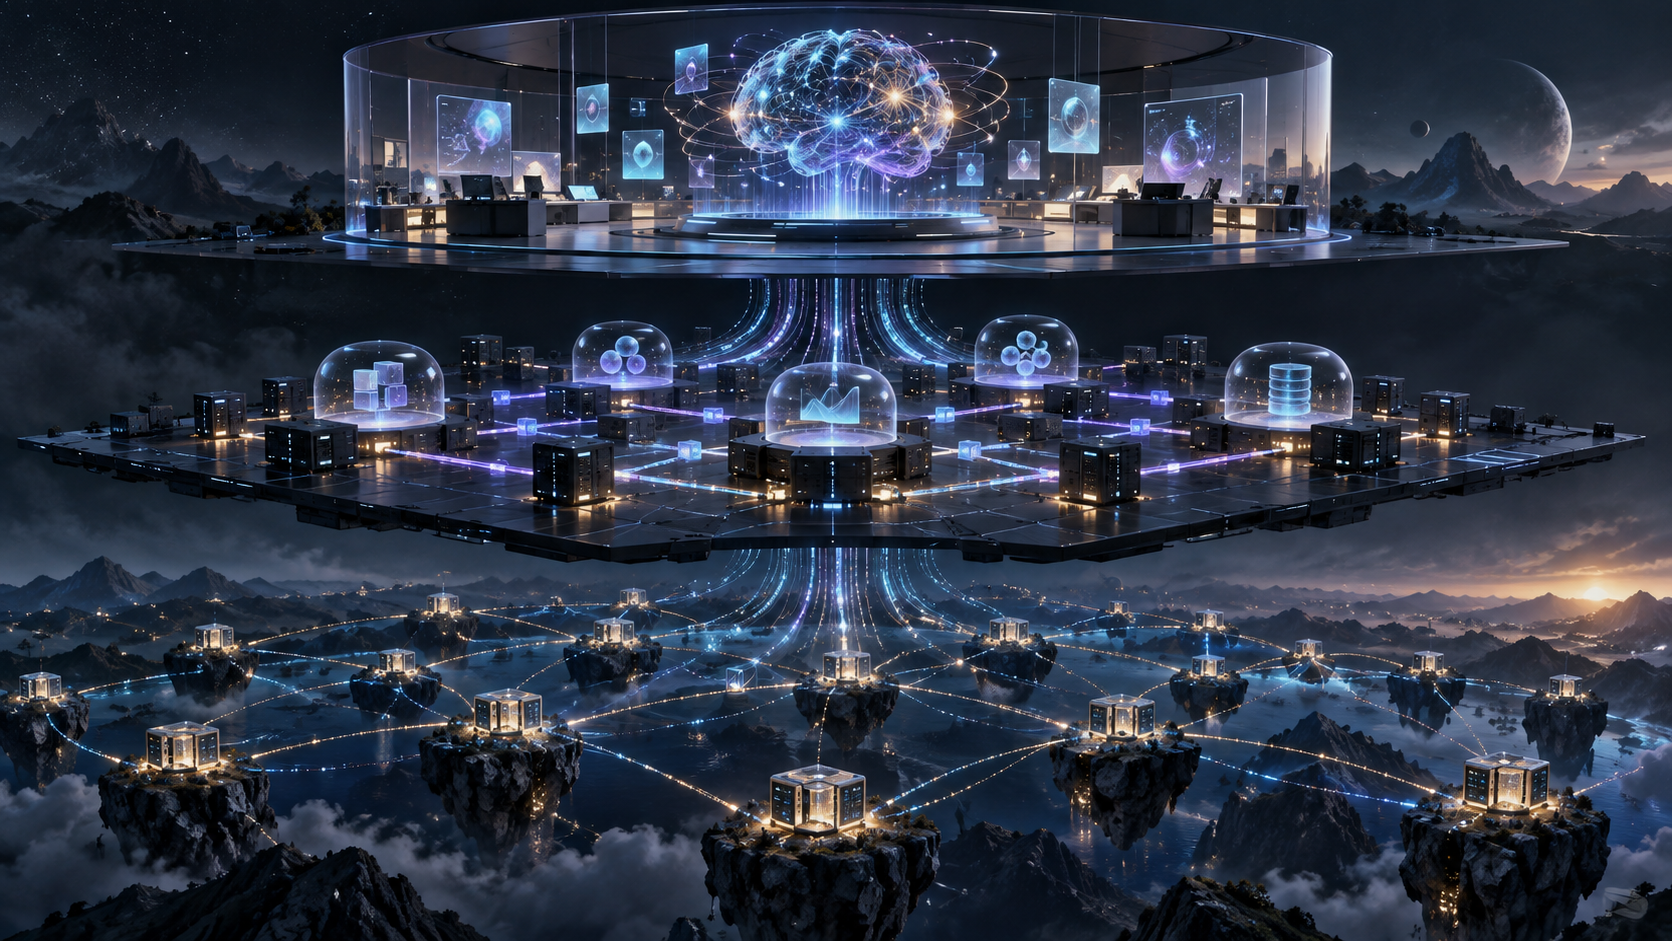
Three unrelated launches on the Hacker News front page describe one emerging architecture. Qwen-Image-2.1 supplies an open model for creation and editing. AX proposes a runtime for isolated, resumable agent tasks. Pirate Face proposes a peer-to-peer permanence layer for model files. Put together, they suggest that “open AI” is becoming a stack rather than a single model-download decision.
At our September 21, 2026, 1:00 p.m. Malaysia-time check, the Qwen discussion had 554 points and 161 comments, AX had 335 points and 129 comments, and Pirate Face had 494 points and 142 comments. Those numbers show concentrated developer attention. They do not validate the products, economics, or security claims.
What happened
Qwen released Qwen-Image-2.1 with a 7B visual-generation component, unified generation and editing, native transparent output, and support for as many as ten reference images. Its role in this stack is capability: it turns prompts and visual inputs into assets.
AX launched an open orchestration layer for stateful agent work. It describes tasks, workspaces, networks, and models as first-class primitives, with an actor runtime beneath them. Its role is execution: it decides where a model-backed job lives, what it can reach, and how it pauses or resumes.
Pirate Face describes a third layer. It mirrors eligible Hugging Face model files into torrents, records SHA-256 checksums, uses Hugging Face as a web seed while the source exists, and expects peers to preserve files if that source disappears. Its role is distribution and continuity. The site’s proposed drop-in API and seeding rewards are explicitly marked as coming soon or planned, not currently complete.
Why it matters
The first wave of open-model enthusiasm compressed all infrastructure questions into “can I download the weights?” That is necessary but insufficient. A usable system also needs reliable inference, an execution boundary, state management, tool access, monitoring, and a way to retrieve the exact artifact later.
Separating those concerns can improve competition. A team might choose Qwen for image work, AX for long-running execution, and a conventional model registry rather than Pirate Face. Another team might use a different runtime while retrieving checksum-verified files from multiple sources. Interchangeable layers reduce the cost of changing one component.
The separation also makes governance legible. A model license governs permitted use. A runtime policy governs data and tool access. A distribution layer governs availability and integrity. Treating all three as “the model” hides important decisions.
Evidence and claims
Qwen’s official post and repository are primary sources for its architecture and features. The post says mixed-granularity attention and KV-cache reuse improve reference-editing efficiency. It presents examples across transparent generation, local editing, identity preservation, and multi-reference composition. We did not independently reproduce its benchmarks, so quality comparisons remain release-team claims.
AX’s site and linked Agent Substrate repository document the control-plane idea. AX claims billions of tasks per cluster and sub-second resumption. Those claims need reproducible external benchmarks. Even if the absolute scale is smaller, the core design question remains valid: idle agents should not reserve full workers, and durable task state should not be improvised by every application.
Pirate Face’s public site explains web seeds, magnet links, checksums, source evidence, and current eligibility rules. Its checksum story can verify that a retrieved file matches the recorded source artifact. That does not prove the model is safe, lawful, unbiased, or free of malicious behavior. Integrity answers “did these bytes change?” not “should these bytes exist or run?”
The three-layer model
Capability layer
The model layer determines what the system can generate or understand. Qwen-Image-2.1 shows pressure toward smaller, more versatile components that handle multiple related tasks. Open artifacts allow local evaluation and custom inference, but they also transfer operational responsibility to the user.
Execution layer
The runtime layer determines how capability becomes action. AX makes workspaces and networks explicit because an agent can touch files, run commands, and call services. That boundary may matter more for security than another point on a model benchmark. An excellent model inside an uncontrolled runtime is an excellent way to make mistakes quickly.
Permanence layer
The distribution layer determines whether the same artifact remains available and identifiable. Central registries are efficient but create dependency on one host, one account system, and one policy regime. Peer-to-peer mirroring can add resilience. It also complicates takedowns, licensing changes, privacy claims, and response to discovered malware.
Practical takeaway
Organizations should write an inventory across all three layers. Record the exact model revision and checksum. Record the runtime image, workspace policy, network allowlist, and model provider. Record where artifacts can be retrieved if the primary host changes access.
Then test layer replacement. Can the model be moved to another inference engine without rewriting the workflow? Can the agent runtime change without losing task state? Can the artifact be restored from a mirror and verified against the approved hash? Portability that exists only in a diagram is not portability.
Security teams should avoid confusing decentralization with trust. A torrent can preserve a vulnerable model forever. A hash can preserve a poisoned artifact perfectly. A sandbox can resume a compromised task reliably. Each layer needs its own review and revocation story.
Limitations and counterarguments
The stack may be too fragmented for many users. Managed providers combine model hosting, runtime, storage, monitoring, and support because integration has real value. Small teams may rationally prefer one accountable vendor over interchangeable parts with separate failure modes.
Open components can also be open in different senses. Source code may be available while weights, training data, or commercial rights remain restricted. A model may be downloadable but impractical to run. An orchestrator may be open but depend on specialized infrastructure. A mirror may preserve files whose licenses do not permit redistribution.
Pirate Face’s permanence goal creates the sharpest governance tension. Resilience against arbitrary deletion can protect research and cultural continuity. It can also frustrate legitimate removal requests. The site’s current MIT/Apache eligibility rules and source-evidence process are governance choices, not universal solutions.
Final verdict
Qwen-Image-2.1, AX, and Pirate Face are not one coordinated platform, and none proves the others. Their simultaneous visibility matters because each attacks a different bottleneck: making capable models, running long-lived agent work, and keeping approved artifacts reachable.
The open AI market is likely to look less like one heroic model and more like Linux infrastructure: layers, interfaces, competing implementations, and arguments about who maintains the pieces. That is messier than a single API. It is also where durable choice can emerge.
Sources
> Want more like this?
Get the best AI insights delivered weekly.
By subscribing, you agree to our Privacy Policy. You can unsubscribe at any time.
> Related Articles
Claude Code Left Secrets in 1,122 GitHub Files—Check This Setting
Apiiro traced exposed credentials to Claude Code permission files. The awkward part: approving a command can preserve the password inside your project.
GPT-6 Cyber Can Build Exploits—But Builders Face a Different Test
OpenAI's GPT-6 Cyber pairs stronger exploit research with tighter scope controls. For builders, access rules and reproducible evidence matter as much as benchmarks.
1,122 GitHub Files Exposed Secrets—What Did “Don't Ask Again” Save?
Apiiro found credentials in 1,122 public Claude Code settings files. A saved approval can preserve the password inside a command—and send it into your next commit.
Most Read
- 1 Kimi K3.1 Pro: China's Open-Weight Model Just Caught the Frontier
- 2 OpenAI Is Buying the Bottleneck: Can Orchestra Bio Cut a 15-Year Drug Timeline?
- 3 1,068 Tokens Per Second: Can Mercury 3 Change How LLMs Generate Text?
- 4 Same Price, Better Coding: How Good Is DeepSeek V4.1 Flash 1017?
- 5 Used OpenCode? Should You Rotate Your API Key After the Console Breach?





Latest News
- Claude Code Left Secrets in 1,122 GitHub Files—Check This Setting
- Gemini Omni 1.2 Flash Makes 15-Second Video Cheaper—Then Comes the Edit
- GPT-6 Cyber Can Build Exploits—But Builders Face a Different Test
- 1,122 GitHub Files Exposed Secrets—What Did “Don't Ask Again” Save?
- Gemini Omni 1.2 Flash Offers $1.05 Clips—What Does That Buy You?
- GPT-6 Cyber Hits 48.5% on ExploitGym—Who Gets the Keys?
Tags
> Stay in the loop
Weekly AI tools & insights.