Authorization-Aware RAG: Enforce Access Control Before Retrieval
A RAG system can leak data before the model answers. Filter retrieval with authoritative permissions, protect caches, and test access boundaries end to end.
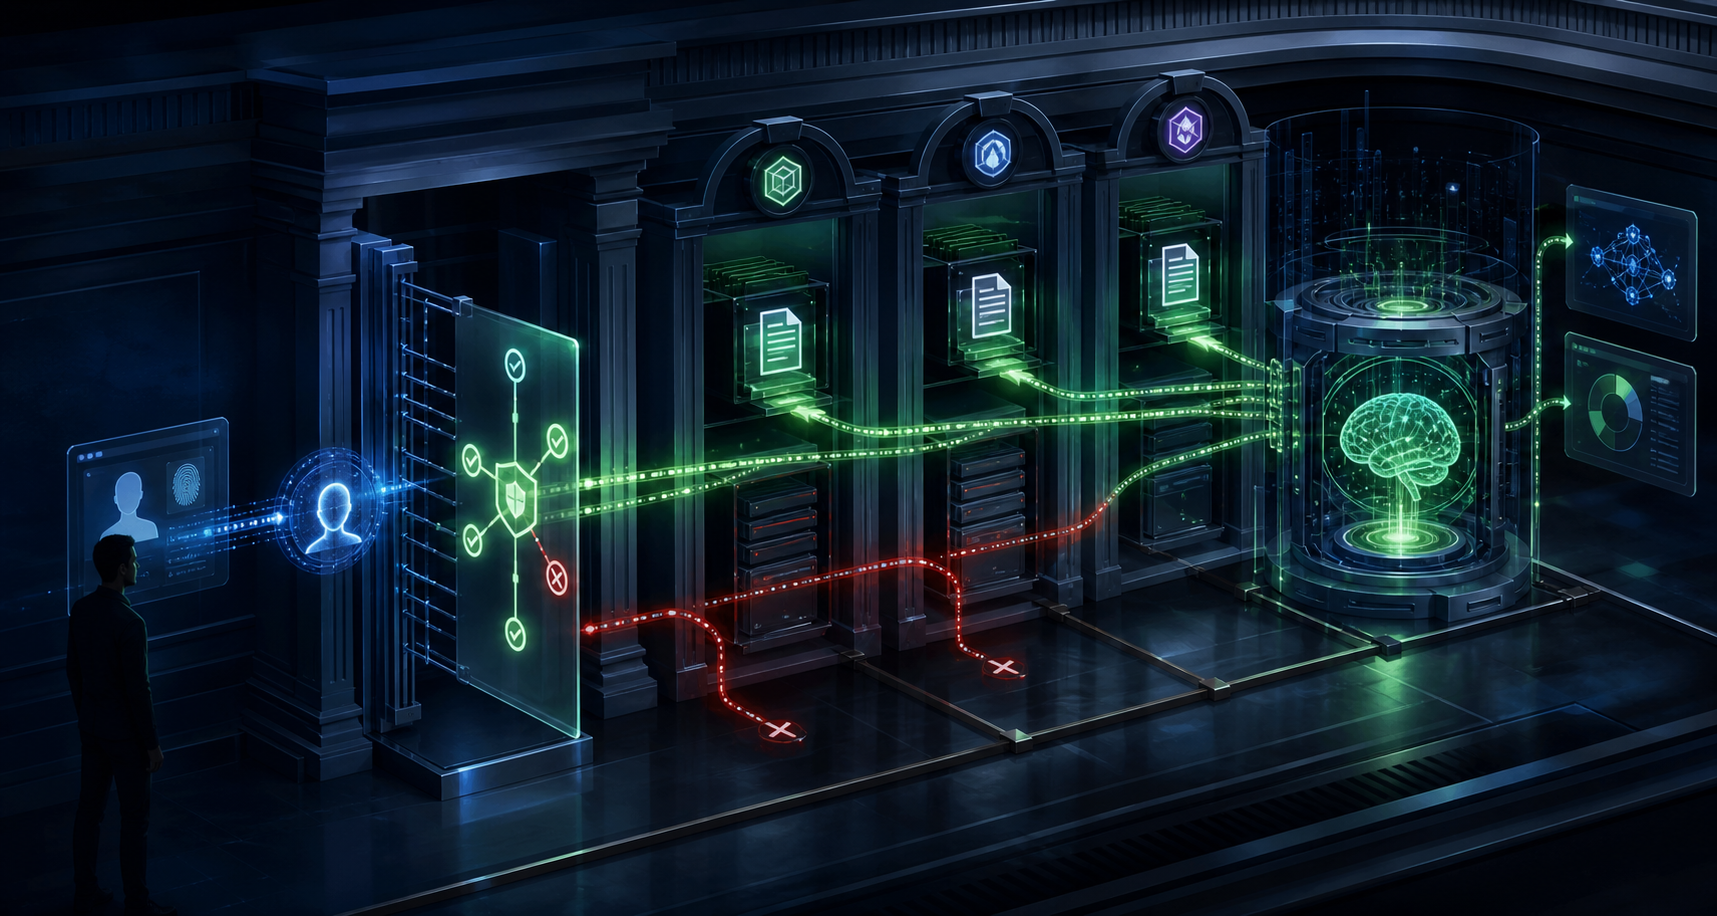
Retrieval-augmented generation can disclose protected information even when the final answer looks harmless. Search results may enter prompts, traces, caches, evaluation datasets, or citations before a model decides what to say. Authorization must therefore constrain retrieval itself—not merely filter generated text.
The core rule is simple: determine what the caller may access using an authoritative policy, then search only within that boundary.
Carry Identity and Context Into Retrieval
A RAG request needs more than a query string. It should carry a verified principal, tenant, roles or attributes, purpose when relevant, and request context such as device or network posture.
Do not trust tenant IDs or document filters supplied only by the model. The application should derive them from authenticated session state and pass a signed or server-side authorization context to the retrieval layer.
const scope = await policy.allowedScope({
  principal: session.userId,
  tenant: session.tenantId,
  action: "document.read",
  context: requestContext
});

const hits = await index.search(query, { filter: scope.filter });
The model may suggest a query, but it never expands scope.filter.
Enforce Permissions Before Ranking
Post-filtering the top results is both unsafe and ineffective. If the vector database retrieves unauthorized documents first, their content may already be exposed to logs or middleware, and removing them can leave too few useful results.
Apply access filters inside the search operation when supported. For highly sensitive systems, separate indexes or namespaces can reduce cross-tenant risk. Replicate permission changes promptly and fail closed when the authorization service is unavailable.
Metadata is security-critical. A document with a missing tenant or classification field should not default to public. Ingestion must validate ownership and access labels before indexing chunks.
Recheck at Use Time
Permissions can change after indexing or between retrieval and action. Re-authorize documents before adding them to the prompt when the cost is acceptable, especially for long-lived sessions or high-risk data.
Treat citations and source previews as disclosures too. A link title, snippet, or filename can reveal confidential facts. The UI should render only sources the current viewer can still access.
Agents that act on retrieved data need a separate authorization decision for the action. Permission to read an invoice does not imply permission to refund it.
Partition Caches and Observability
Cache keys must include every authorization dimension that changes results: tenant, principal or permission fingerprint, policy version, and relevant context. A global cache keyed only by normalized question can return one user’s answer to another.
Prompt traces, retrieved chunks, and model outputs inherit the sensitivity of their inputs. Redact where possible, encrypt storage, restrict operator access, and use short retention. Evaluation exports must preserve access boundaries instead of creating a shadow corpus.
Invalidate cached results when permissions change. If immediate invalidation is difficult, use short time-to-live values and verify access again before display.
Test the Boundary, Not Just Answer Quality
Build adversarial tests with two tenants, overlapping terminology, revoked permissions, malformed metadata, cache hits, and policy-service outages. Assert that unauthorized document identifiers never reach prompts, traces, citations, or responses.
Test horizontal access between peer users and vertical access between roles. Include indirect prompt injection that asks the model to remove filters or call retrieval tools with a different tenant.
Log authorization decisions with policy version and resource identifiers, but avoid logging sensitive content. Monitor denied retrieval attempts, missing labels, cross-tenant cache keys, and stale-policy errors.
Authorization-aware RAG is an architecture property, not a prompt instruction. When identity, policy, retrieval, caching, and observability share the same boundary, the model can be useful without becoming an alternate path around the permissions the rest of the product already enforces.
Sources
> Want more like this?
Get the best AI insights delivered weekly.
By subscribing, you agree to our Privacy Policy. You can unsubscribe at any time.
> Related Articles
pgvector Can Return 4 of Your 10 Matches—Where Did the Rest Go?
A filtered vector search can quietly starve your AI app of evidence. pgvector has a fix, but builders need to measure recall and latency before trusting it.
Agent Memory Consolidation Scheduling: When to Merge, Summarize or Forget
Your agent doesn't need more memory — it needs a maintenance schedule. Here's how to build merge, summarize, and decay policies that keep long-term agents sharp instead of senile.
LLM Output Schema Evolution: Migrating Producers and Consumers Without a Flag Day
Your JSON schema will change. Here's how to evolve LLM output contracts safely — with dual readers, shadow validation, and staged rollouts instead of a risky big-bang cutover.
Most Read
- 1 Kimi K3.1 Pro: China's Open-Weight Model Just Caught the Frontier
- 2 OpenAI Is Buying the Bottleneck: Can Orchestra Bio Cut a 15-Year Drug Timeline?
- 3 1,068 Tokens Per Second: Can Mercury 3 Change How LLMs Generate Text?
- 4 Same Price, Better Coding: How Good Is DeepSeek V4.1 Flash 1017?
- 5 Used OpenCode? Should You Rotate Your API Key After the Console Breach?





Latest News
- Claude Code Left Secrets in 1,122 GitHub Files—Check This Setting
- Gemini Omni 1.2 Flash Makes 15-Second Video Cheaper—Then Comes the Edit
- GPT-6 Cyber Can Build Exploits—But Builders Face a Different Test
- 1,122 GitHub Files Exposed Secrets—What Did “Don't Ask Again” Save?
- Gemini Omni 1.2 Flash Offers $1.05 Clips—What Does That Buy You?
- GPT-6 Cyber Hits 48.5% on ExploitGym—Who Gets the Keys?
Tags
> Stay in the loop
Weekly AI tools & insights.