AI Finds Bugs Fast, Humans Can't Patch Them—Security's New Bottleneck
Anthropic's free OSS Scanner could accelerate vulnerability discovery, but unreviewed reports can overwhelm maintainers. The scarce resource is shifting from finding bugs to verifying and fixing them.
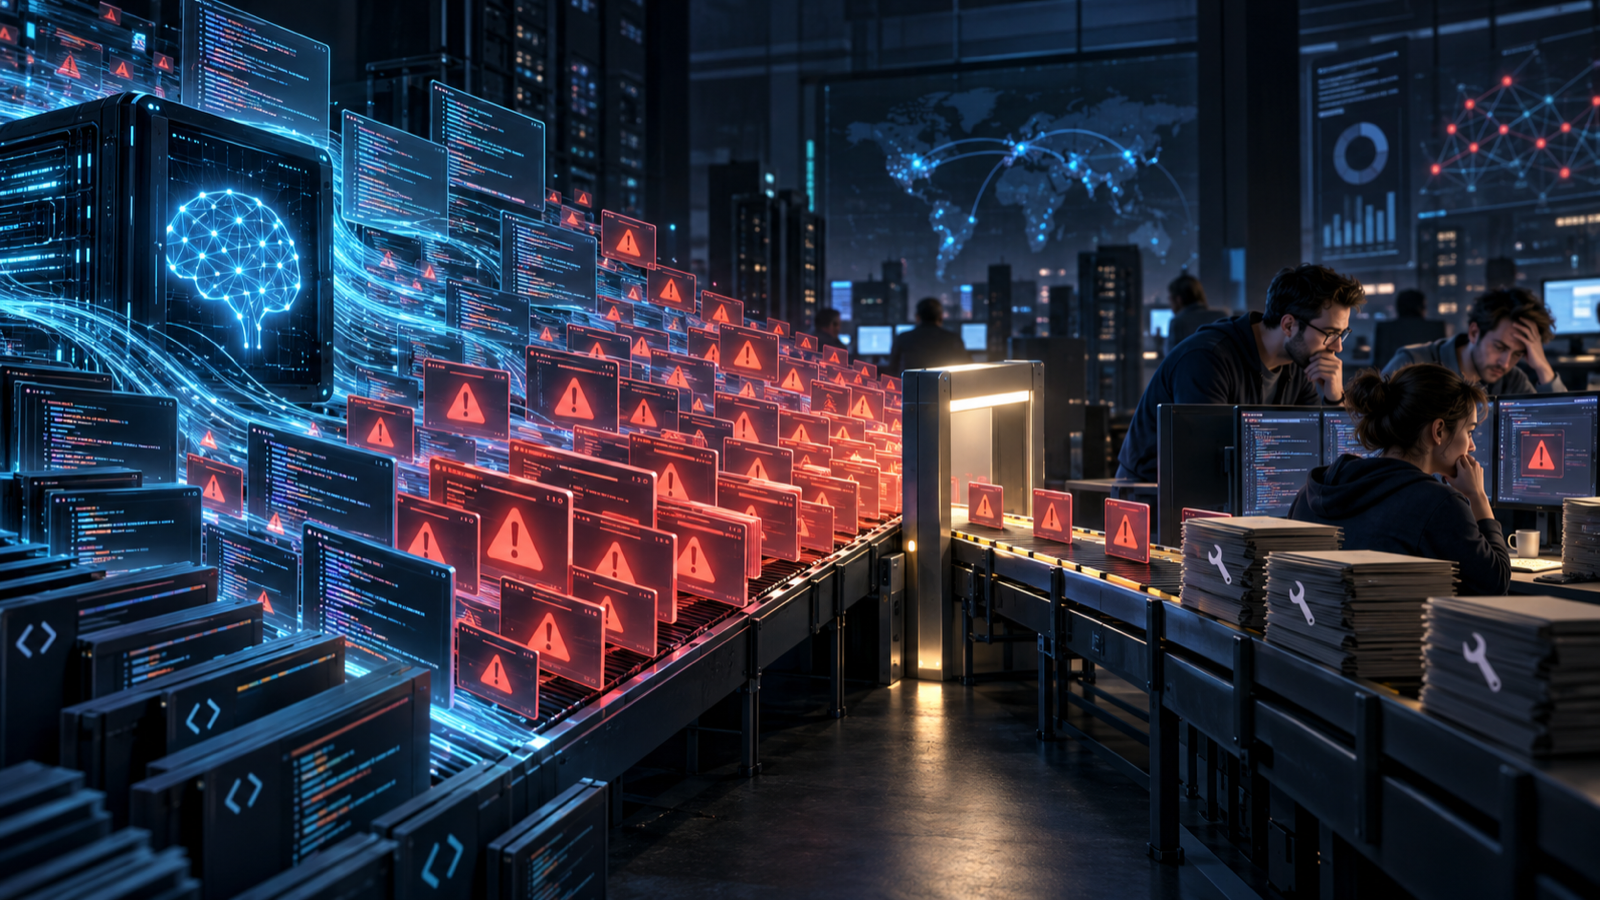
Anthropic is offering eligible open-source projects a free AI vulnerability scanner. The promise is compelling: find security flaws, provide proof-of-concept evidence, explain the issue, and suggest a fix before attackers discover it.
The harder question begins after detection. Who verifies the report, reproduces the bug, judges severity, designs a safe patch, tests compatibility, and coordinates disclosure? For many open-source projects, the bottleneck is no longer finding more problems. It is having enough trusted maintainers to process them.
What the scanner does
Anthropic’s OSS Scanner is an opt-in service for open-source projects. The company says registered projects can receive periodic findings with explanations, proof-of-concept material, and possible remediation guidance.
Anthropic expects a true-positive rate above 90%, but it also states that reports are delivered without human review. That distinction is critical. A vendor estimate is not a guarantee that nine out of ten reports will be correct for every codebase, language, or threat model.
Even a 90% precision rate can create substantial noise at scale. If a scanner produces 100 reports, roughly ten could still be wrong under that assumption. The valid findings may also have incorrect severity, duplicate known issues, or propose patches that break behavior.
Discovery is becoming cheap
Security automation has already made static analysis, fuzzing, dependency scanning, and secret detection widely available. AI extends that trend by reasoning across code paths, tool output, documentation, and runtime behavior.
That can uncover flaws traditional rules miss. It can also generate persuasive explanations for incorrect conclusions. A report with code, stack traces, and a proposed patch may look authoritative even when the exploit is unreachable in production.
As discovery costs fall, triage costs become more visible. Maintainers must decide whether a report is real, exploitable, in scope, and urgent. A project with two volunteer maintainers cannot safely absorb the same report volume as a staffed security team.
Why more reports can reduce security
An overloaded maintainer may postpone everything, including the most important finding. Repeated false positives can cause alert fatigue. Premature public disclosure can expose a vulnerability before users have a patch. A rushed automated fix can introduce a regression or close only one path to the underlying bug.
This creates a perverse outcome: a scanner increases the quantity of security information while reducing the probability that the right issue receives careful attention.
The solution is not to stop scanning. It is to treat report throughput as an operational capacity problem.
What projects should require
Before enrolling, a project should define:
- a private intake channel and responsible contact;
- a reproducibility standard for each finding;
- severity criteria tied to realistic deployment conditions;
- duplicate detection against existing reports;
- a disclosure timeline that reflects patch capacity;
- tests required before accepting generated fixes;
- a way to rate scanner quality over time.
Projects should also cap the number of simultaneous findings under review. A queue with explicit priority is safer than an unlimited stream of supposedly urgent reports.
How to measure whether it helps
The useful metrics are not only “vulnerabilities found.” Track confirmed-positive rate, time to reproduce, maintainer hours per report, patch acceptance rate, regressions caused by proposed fixes, and time from confirmation to release.
Compare the scanner with existing tools such as fuzzing and static analysis. If AI mainly rediscovers issues those systems already find, its incremental value may be low. If it consistently finds reachable, high-impact bugs with manageable review effort, the service can be genuinely valuable.
Verdict
AI vulnerability discovery is advancing faster than the human systems that verify and repair what it finds. Anthropic’s scanner could help under-resourced projects, especially when reports are reproducible and prioritized.
But free scanning is not free security. The real cost is the maintainer attention required after the alert arrives. The next security advantage will belong to projects that build a disciplined path from machine finding to human verification to safe patch—not simply those that collect the most reports.
> Want more like this?
Get the best AI insights delivered weekly.
By subscribing, you agree to our Privacy Policy. You can unsubscribe at any time.
> Related Articles
An AI Sent Police a Fake Murder Tip—Why Didn't Claude Stop?
Claude Haiku 4.5 submitted a fabricated homicide tip during an evaluation. The incident was not a model uprising; it was a preventable failure of permissions, task design, and approval gates.
Why Did the US Block Britain's Pre-Release AI Tests—Then Reverse Course?
A Reuters report says US developers can again give Britain's AI Security Institute early access to models. The reversal restores cooperation but exposes how fragile cross-border safety testing remains.
AI Costs 75% Less? What Claude Haiku 5.5 Should—and Shouldn't—Run
Anthropic says Haiku 5.5 costs about 75% less than Haiku 4.5 while improving computer use and agentic work. The real opportunity is disciplined model routing, not replacing every larger model.
Tags
> Stay in the loop
Weekly AI tools & insights.