AI Systems Need Three Trust Layers: Verifiable Work, Managed Permissions, and Private Credentials
A cipher-solving agent, GitHub's enterprise controls, and Signal's zkgroup work point to the same production lesson: intelligence needs enforceable trust boundaries.
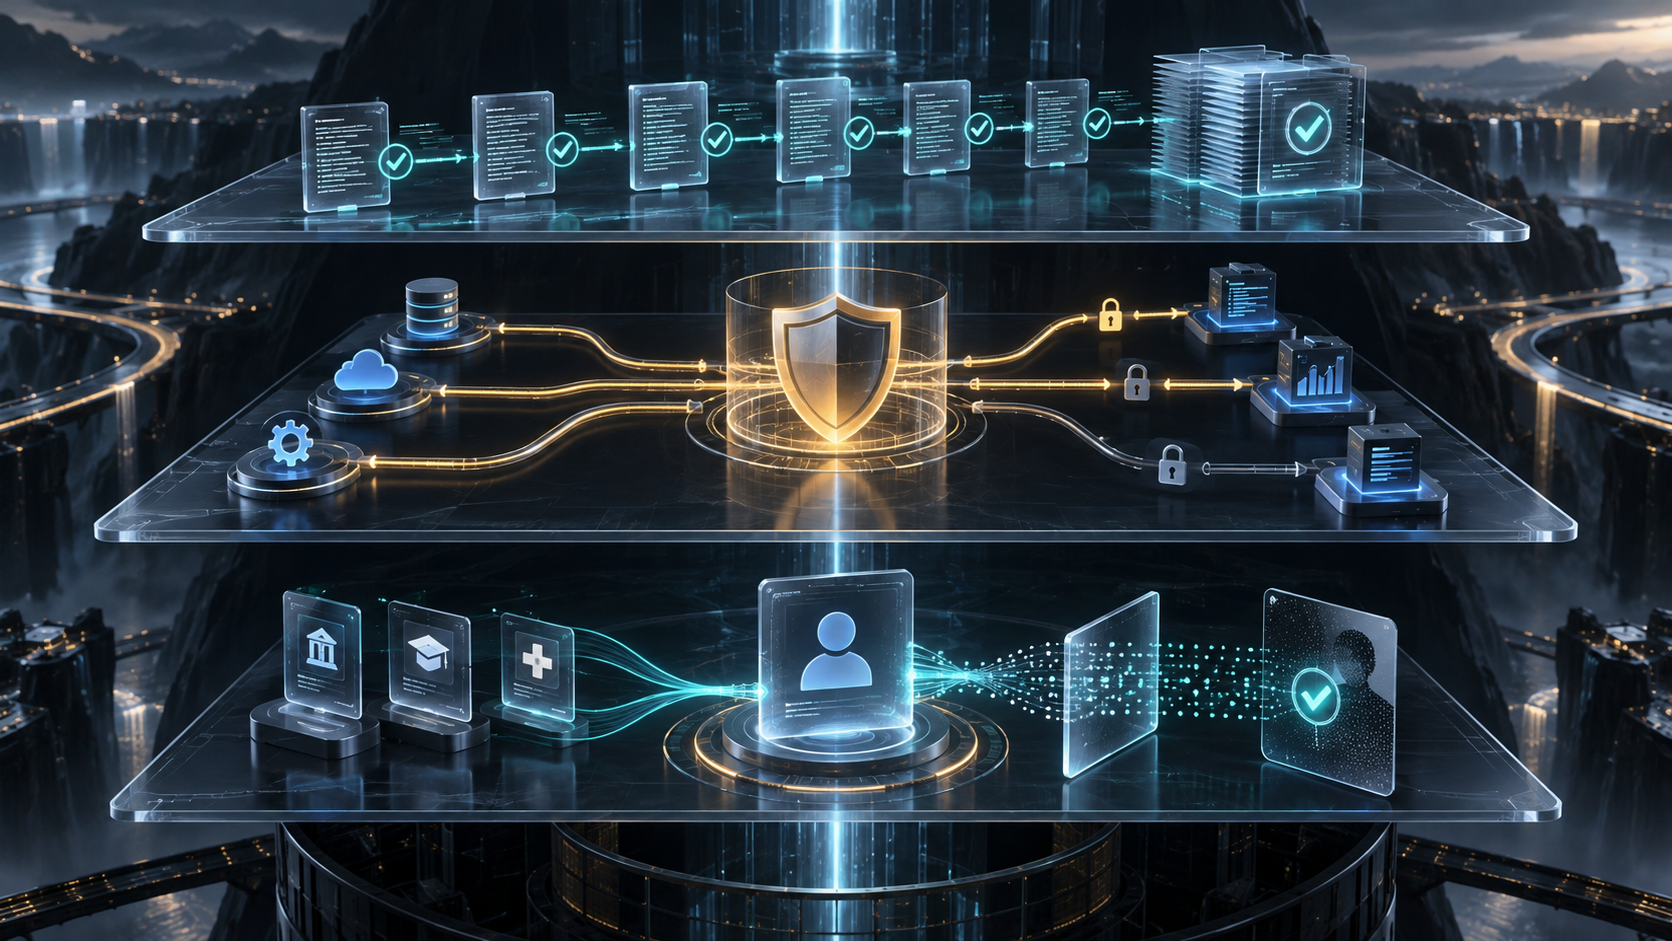
Three unrelated technology stories this week reveal the same architectural shift. A Claude agent reportedly solved a historical cipher by leaving a reproducible coordinate trail. GitHub gave enterprises centrally managed deny/ask/allow controls for Copilot agent operations. Signal’s phone-numberless account work uses private credentials to prove eligibility without carrying a phone number through the system.
Together they describe a production trust stack: verify the work, constrain the action, and minimize the identity disclosed. Model intelligence helps choose a path. It does not replace any of those layers.
Layer one: make outputs independently verifiable
Vals’ Cyphral Distich result is compelling because the proposed answer can be checked against a source. The method maps each number to a word in a corresponding passage and extracts an initial. A reviewer does not need to trust the model’s explanation or the operator’s enthusiasm; they can rerun the transformation.
Most agent tasks are messier, but the principle transfers. Code agents can run tests and static analysis. Research agents can provide exact source spans and calculation notebooks. Data agents can publish row counts, checksums, and reconciliation totals. Deployment agents can query the public endpoint after a release.
The verifier should be outside the generation loop. If the same model writes the answer and grades it with a vague prompt, shared blind spots survive. Deterministic checks are best where possible; a human or separate evaluation system should review judgment-heavy claims.
Verification also changes task design. “Write a good report” has no crisp terminal condition. “Use these sources, account for every record, pass these policy checks, and produce URLs that return 200” gives the agent observable state.
Layer two: permissions must live below the prompt
GitHub’s September 9 controls let enterprise administrators classify shell commands, file reads and edits, and network domains as blocked, approval-required, or allowed. GitHub says centrally managed restrictions cannot be weakened by user settings, workspace settings, auto-approval, or saved approvals.
That placement is essential. A prompt such as “never upload secrets” is a behavioral request to a probabilistic system. An egress deny rule is an enforcement mechanism. Both are useful, but only the second remains reliable when the prompt is misunderstood, truncated, or attacked by untrusted content.
Production agents need capability boundaries that reflect consequences. Reading a public document is not equivalent to editing a repository. Editing a local draft is not equivalent to pushing to production. Sending an external message is not equivalent to preparing one for review. A useful policy separates those operations instead of giving the agent one broad “tools enabled” state.
Managed policy also needs context. Finance may permit reads from a reporting database while engineering permits a staging deployment. The goal is not the most restrictive global rule. It is the smallest capability set that completes a specific job.
Layer three: prove entitlement without overexposing identity
Signal’s planned paid phone-numberless registration highlights a different boundary. The service needs to control abuse and establish that an account completed an authorized issuance flow, but a permanent phone number reveals more than that fact.
Private credentials and zero-knowledge proofs offer a way to separate the check from later use. In simplified terms, an issuer can confirm an entitlement and give the user a credential; the user later proves possession or a property without replaying all identifying inputs.
Agent systems will need similar patterns. An agent may need proof that a user can access a dataset, approve spending within a limit, or act for an organization. Passing the raw employee record, payment receipt, or master token into every tool call expands the breach surface. Short-lived, scoped, privacy-preserving credentials reduce what each component sees.
This is not anonymity magic. Network metadata, logs, payment processors, and recovery systems may still reveal relationships. Protocol claims must be tested against the entire operating system.
How the layers work together
Imagine an agent preparing and publishing a corporate filing summary. The verification layer checks that every number reconciles to an official filing and that links resolve. The permission layer allows reading filings and writing a draft but requires approval before publication. The credential layer proves the requester belongs to the communications team without exposing a broad directory profile to every service.
Failure in one layer should not collapse the others. A correct summary should still be blocked from publishing if authorization is missing. An authorized agent should still fail if figures do not reconcile. A verified and authorized action should still use the least identifying credential available.
This structure also improves incident response. Logs can show whether the failure was epistemic, operational, or identity-related: the agent produced an unsupported claim, crossed a policy boundary, or used an invalid entitlement.
Practical implementation checklist
Start by listing consequential actions and their independent verifiers. Define what can be checked before execution and what must be checked afterward. Give each tool a narrow contract, explicit input schema, idempotency behavior, and a way to report evidence.
Next, build policy outside model context. Use deny/ask/allow rules for files, commands, domains, data classes, and external communications. Ensure lower-level workspace settings cannot silently widen centrally defined restrictions.
Finally, redesign credentials. Prefer short-lived tokens, audience restriction, purpose limitation, and revocation. Keep secret material out of transcripts and model-visible logs. Where a service only needs proof of a property, evaluate anonymous or selective-disclosure credentials rather than forwarding the source identity record.
NIST’s AI Risk Management Framework offers a broader governance vocabulary, but teams still need concrete controls at runtime. A policy document that cannot stop a tool call is not a guardrail.
Limitations
These three cases operate in different domains. Vals reports a research experiment, GitHub documents a commercial enterprise feature, and Signal’s registration path is still evolving. Their combination is an architectural interpretation, not evidence that the products share one implementation.
Zero-knowledge systems and agent sandboxes require expert review. Misconfigured logging, recovery, domain wildcards, or approval caching can undermine the intended boundary. Verification can also be gamed when metrics become targets.
Final verdict
The next generation of useful AI systems will be judged less by whether an agent can produce a clever answer and more by whether the environment can prove what happened, prevent unauthorized action, and reveal only the identity data required. Verification, permission, and private credentials are separate layers. Mature systems will need all three.
Sources
> Want more like this?
Get the best AI insights delivered weekly.
By subscribing, you agree to our Privacy Policy. You can unsubscribe at any time.
> Related Articles
RAG Query-Rewriting Evaluation: Prove the Rewrite Finds Better Evidence
Query rewriting often sounds smarter while retrieving worse evidence. Evaluate rewrites against relevant documents, failure slices, and final grounded answers before shipping them.
RAG Retrieval Diversity: Stop Near-Duplicate Chunks From Crowding Out the Answer
Top-k retrieval can return five versions of the same paragraph and miss the one document that changes the conclusion. Add deduplication and diversity with measurable tradeoffs.
Numeric Precision in Structured LLM Output: Stop Rounding From Becoming a Production Bug
Valid JSON can still corrupt money, measurements, IDs, and percentages. Design schemas and validators so an LLM never gets to improvise numeric precision.
Tags
> Stay in the loop
Weekly AI tools & insights.